
October 23, 2026
12 mins read
Webflow Campaigns Explained: Features, Benefits, and What Marketers Need to Know in 2026
Explore appsrow with AI
Website security is no longer just a concern for developers and IT teams. It directly affects business continuity, customer trust, search visibility, and the reliability of digital marketing operations. A vulnerability in a widely used technology can create risks across thousands of websites, even when individual businesses have followed common security practices.
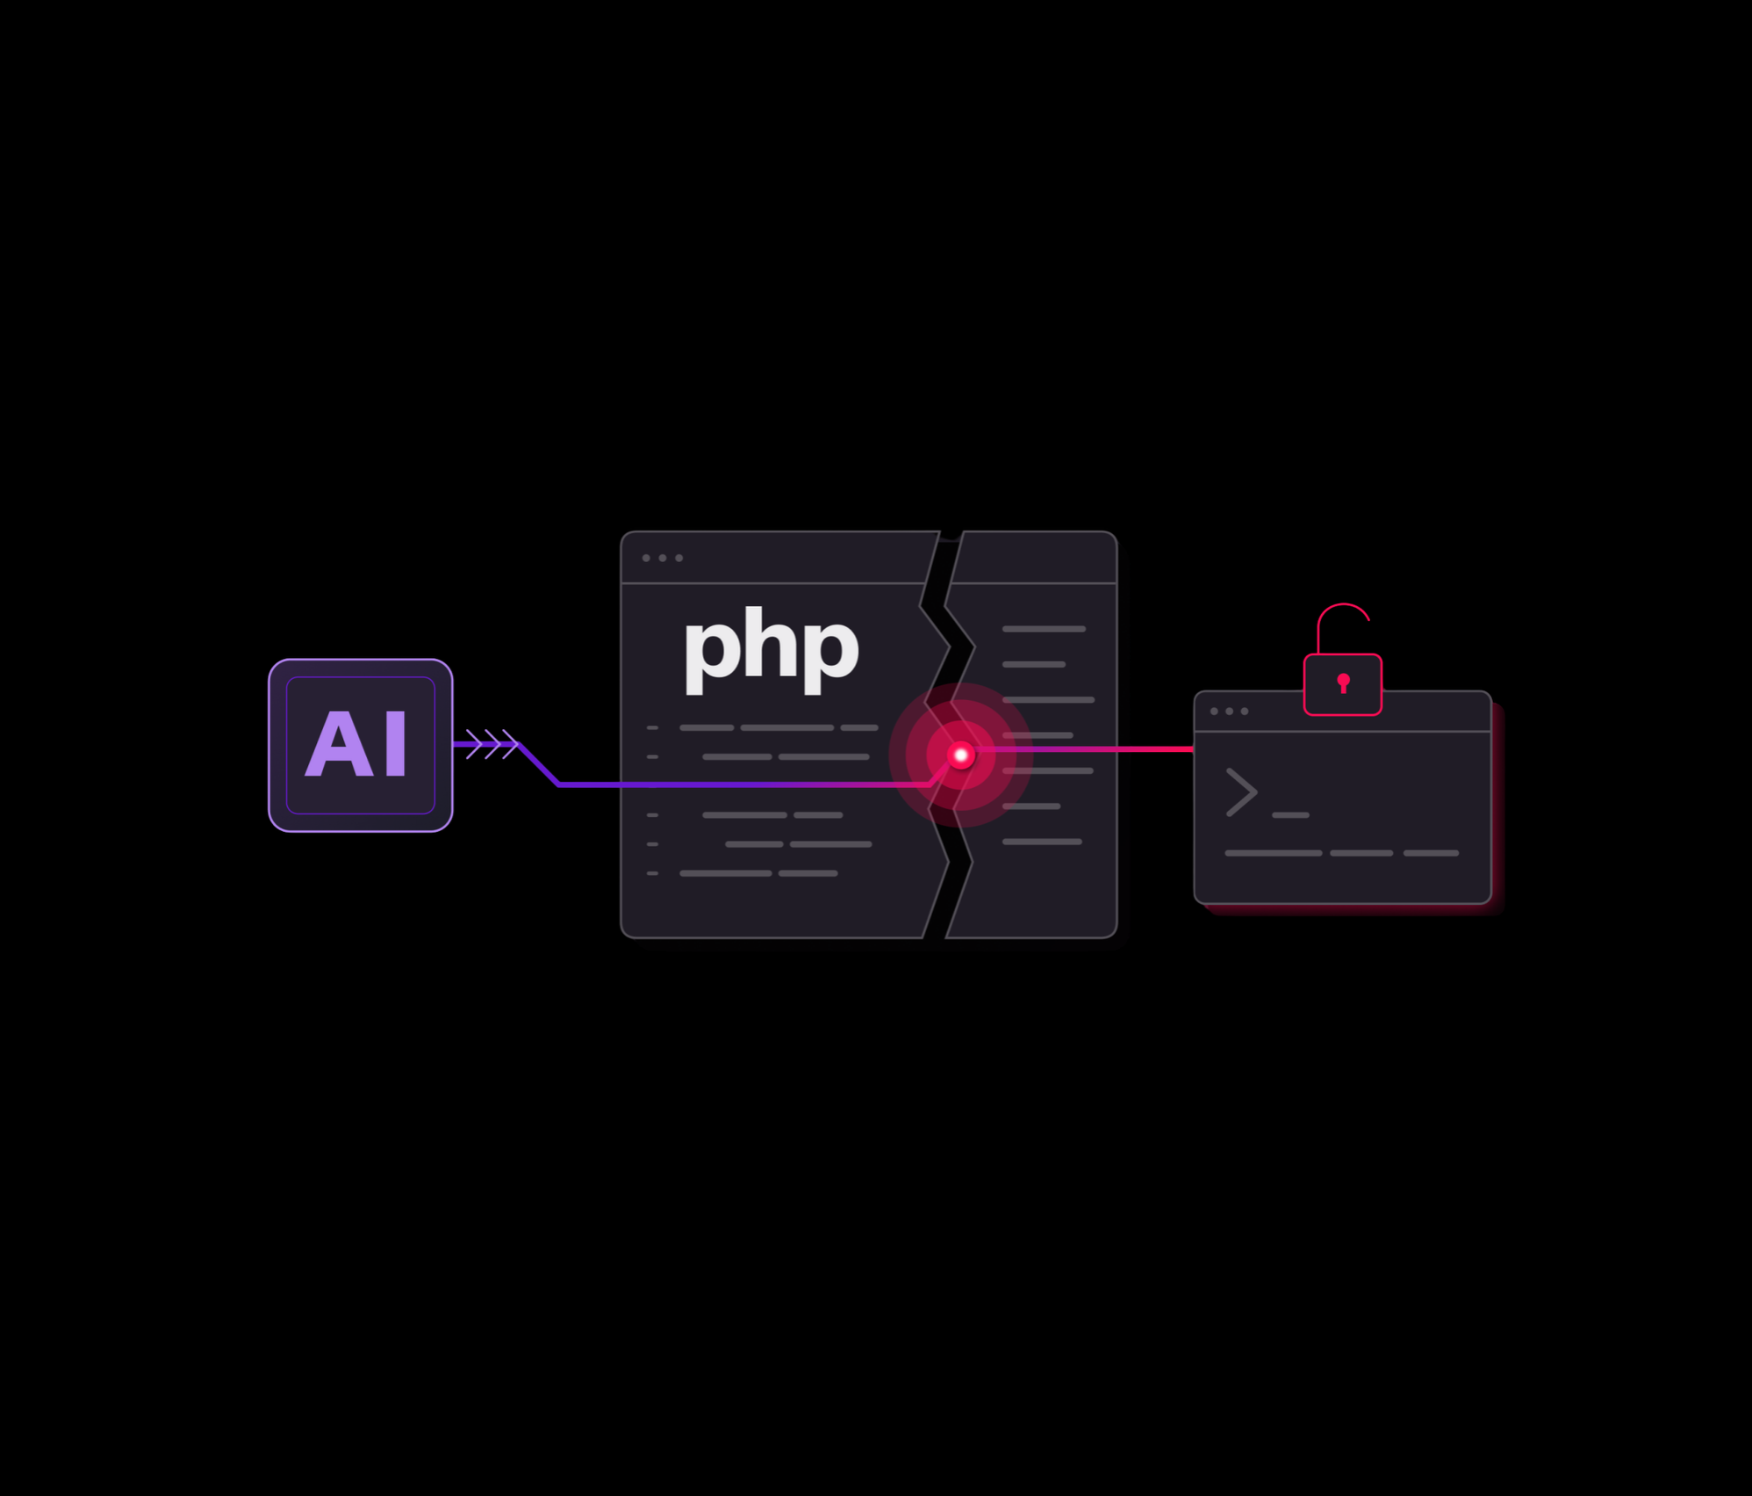
The PHP2Shell vulnerability, disclosed by Wiz Research on October 21, 2026, highlights this challenge. Researchers identified critical flaws in PHP's core runtime that could allow unauthenticated remote code execution and sensitive process-memory disclosure on affected systems. The vulnerabilities were demonstrated against popular PHP-powered platforms, including WordPress, Drupal, and Joomla.
For businesses running PHP-based websites, the announcement is a reminder to review server software, security patches, hosting responsibilities, and incident response procedures.
It also raises an important question for companies choosing a website platform: how much security maintenance should their internal teams manage themselves?
This is where Webflow deserves attention. Its managed hosting model removes much of the customer-side responsibility for maintaining a PHP runtime, applying operating-system patches, and managing a traditional website server. Although no platform eliminates every security risk, reducing the number of components a business must maintain can simplify website operations.
In this article, we explain PHP2Shell, examine its implications for website owners, and explore why Webflow can be a practical choice for businesses seeking a more manageable website security model.
PHP2Shell is the name associated with two critical vulnerabilities discovered in PHP's core runtime. According to Wiz Research, the issues involve memory-safety failures that can leave PHP in an inconsistent internal state after certain fatal errors.
The vulnerabilities are tracked as:
Wiz reported that successful exploitation could enable attackers to execute code remotely without authentication on affected systems. The research also demonstrated that sensitive information, including passwords, tokens, and API keys, could potentially be disclosed from PHP worker memory.
The critical distinction is that these flaws exist in the PHP runtime itself, rather than necessarily in the website application's own code.
This means that updating a CMS theme or removing a vulnerable plugin is not sufficient to correct an affected PHP runtime. The underlying PHP installation must receive the appropriate security fix.
The PHP project released patched versions on October 21, 2026, including PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Organizations should verify the appropriate fix for their actual runtime and operating-system distribution, including any vendor-provided security backports.
Source: Wiz Research's PHP2Shell technical report.
PHP powers a large portion of the web. It is commonly used by content management systems, e-commerce platforms, and custom web applications. A serious vulnerability in the runtime can therefore affect a broad range of businesses.
The potential consequences extend beyond temporary website downtime.
Remote code execution vulnerabilities can allow attackers to run commands on affected systems. Depending on the server's permissions and configuration, this could lead to unauthorized access to files, applications, or other resources.
For businesses, a compromised server can disrupt normal operations and require significant recovery work.
Wiz demonstrated that PHP2Shell could expose sensitive data held in process memory. Depending on the environment, this could include authentication tokens, credentials, or API keys.
Businesses should treat credentials and secrets as sensitive assets and investigate potential exposure if their systems may have been compromised.
Attackers who gain sufficient access may alter website content, interfere with application behavior, or disrupt service availability.
For marketing teams, these incidents can interrupt lead generation, damage brand credibility, and create unexpected recovery costs.
Security incidents often require developers, hosting providers, and IT administrators to coordinate emergency updates, assess exposure, review logs, and restore affected systems.
The operational burden can be especially challenging for small teams that do not have dedicated infrastructure specialists.
PHP2Shell affects vulnerable PHP runtimes, not every website on the internet.
Wiz demonstrated exploitation against WordPress, Drupal, and Joomla environments. However, the vulnerability exists in PHP itself, so the risk is not limited to those content management systems.
Exposure depends on factors such as the PHP version, deployment architecture, configuration, and whether the relevant vulnerability has been fixed.
Potentially affected environments include:
Updating the CMS alone does not resolve a vulnerability in the PHP runtime. Website owners should ask their hosting provider or technical team to verify the actual runtime version and confirm that the appropriate security fix has been applied.
Businesses should also investigate whether any exposed credentials require rotation and whether suspicious activity occurred before patching.
This is an important distinction for businesses considering Webflow as their website platform.
Webflow's core hosted website services are not built on PHP, according to Webflow's published security information referenced in coverage of the incident. As a result, a standard Webflow-hosted website is not exposed to PHP2Shell through a customer-managed PHP runtime in the way an affected PHP application can be.
Webflow also manages the underlying hosting environment for its standard hosted sites, reducing the need for customers to maintain server software and apply routine infrastructure patches themselves.
For businesses, this changes the operational responsibility involved in website maintenance.
With a traditional PHP-based website, the owner or hosting provider must ensure that the PHP runtime is updated, supported, and appropriately configured. With standard Webflow hosting, customers do not manage a PHP installation for their site.
However, this does not mean Webflow is immune to every security threat. Account compromise, insecure third-party services, malicious or vulnerable custom scripts, misconfigured integrations, and weaknesses in external applications can still introduce risk.
Organizations using Webflow should evaluate their complete digital environment rather than treating any website platform as a guarantee of security.
The PHP2Shell incident illustrates the importance of understanding who is responsible for maintaining the software that powers a website.
Webflow provides managed hosting, meaning customers do not need to maintain a traditional web server or independently update a PHP runtime for standard Webflow-hosted sites.
Webflow's hosting documentation describes a managed service that includes SSL certificate provisioning and hosting infrastructure designed to scale with traffic. Its security materials also describe ongoing security practices and infrastructure protections.
For businesses that prioritize marketing agility, this model offers several operational advantages.
Businesses running self-managed PHP websites must account for runtime updates, operating-system security patches, server configuration, and compatibility testing.
With Webflow's standard managed hosting, much of that underlying infrastructure maintenance is handled by the platform. Teams can spend less time coordinating routine server maintenance and more time improving the website.
Every additional component that a business must configure and maintain introduces operational responsibilities.
A traditional website stack may involve a server, PHP runtime, CMS, themes, plugins, databases, and third-party extensions. Webflow provides an integrated website-building and hosting platform that reduces the number of these components customers must manage directly.
This does not eliminate dependencies. Custom scripts, external services, APIs, and integrations still need appropriate security reviews.
HTTPS protects data transmitted between a website and its visitors. Webflow hosting includes SSL/TLS certificates, helping businesses establish encrypted connections without having to manage certificate installation manually for standard hosted sites.
HTTPS is essential, but it should not be confused with complete application security. Encryption protects data in transit; it does not prevent every possible attack.
Webflow maintains its hosting infrastructure and publishes information about its security practices through its security resources and Trust Center.
For businesses without dedicated infrastructure teams, relying on a managed platform can simplify maintenance responsibilities. Organizations should still evaluate the platform's security documentation, compliance requirements, access controls, and service terms before making a decision.
Choosing between Webflow and a traditional PHP-based website involves more than comparing design capabilities or hosting costs. It also requires understanding which responsibilities remain with the business.
The table compares typical operational responsibilities, not a guarantee that one platform is secure in every situation. Managed hosting reduces some maintenance tasks, but businesses remain responsible for their accounts, data handling, third-party dependencies, and the security of their own workflows.
PHP2Shell is not, by itself, a reason every WordPress website should migrate. Applying the relevant security patch and maintaining a properly configured PHP environment can address this particular vulnerability.
However, the incident may encourage businesses to review whether their current website architecture creates more maintenance work than they want to manage.
WordPress remains a flexible platform with a broad ecosystem. Its security depends on the PHP runtime, hosting environment, core software, themes, plugins, access controls, and maintenance practices.
Webflow offers a different model that combines visual website development with managed hosting. For marketing-led organizations, this can simplify day-to-day website operations and reduce reliance on infrastructure maintenance for routine publishing.
A migration may be worth considering when a business wants to:
A migration should still be evaluated against business requirements, including complex functionality, integrations, e-commerce needs, content architecture, compliance obligations, and long-term platform costs.
For organizations evaluating a platform change, Webflow migration services can help assess the existing website, content, functionality, URLs, integrations, and SEO considerations before implementation.
If your website isn't easy to understand, you're giving away opportunities
before the conversation even starts.
Get a free review of how your website appears to AI-powered search and discovery tools.
Moving to Webflow is not simply a matter of copying pages from one platform to another. A successful migration or new website project should account for the business's content, technical requirements, integrations, access controls, and long-term maintenance needs.
AppsRow helps businesses plan and implement Webflow websites with attention to usability, maintainability, and the needs of marketing and business teams.
A well-structured website can make future changes easier while reducing unnecessary technical complexity.
AppsRow's Webflow development services support businesses that need scalable website structures, reusable components, and custom functionality appropriate to their requirements.
A maintainable architecture also makes it easier to review where third-party scripts, integrations, and external services are introduced.
Security is only one part of a successful website. Businesses also need a website that communicates clearly, performs well, and helps visitors complete their intended actions.
Through Webflow website design, businesses can develop a more consistent user experience while creating a structure that supports ongoing content updates and marketing activities.
Websites often connect to CRMs, analytics platforms, marketing automation tools, payment services, and other external applications. Each connection introduces its own configuration and access considerations.
AppsRow's Webflow integrations services can help businesses connect their website with relevant systems while considering functionality, data flow, and ongoing maintenance.
Third-party services should be reviewed individually because a managed website platform does not automatically secure every connected system.
Launching a website is not the end of the maintenance process. Teams should periodically review access permissions, custom scripts, external dependencies, forms, integrations, and publishing workflows.
Businesses can explore AppsRow's Webflow maintenance services to support ongoing website improvements and reduce the risk of issues going unnoticed.
A website migration can affect organic traffic if URLs, redirects, metadata, structured data, or content relationships are not handled correctly.
AppsRow's Webflow SEO services can support the technical and content considerations that help preserve search visibility during website changes.
Security and SEO serve different purposes, but both contribute to the reliability and long-term performance of a business website.
Although Webflow reduces the burden of managing underlying hosting infrastructure, businesses should still follow good security practices.
Use strong, unique passwords and enable two-factor authentication or single sign-on where available. Access to the Webflow account should be restricted to authorized people.
Remove access for former employees, contractors, and agencies when it is no longer required. Give team members only the permissions necessary for their roles.
Analytics tags, chat widgets, marketing scripts, and external libraries can introduce risks independently of the hosting platform. Review their source, purpose, permissions, and ongoing need.
Confirm that connected services use secure authentication and that API keys or tokens are not unnecessarily exposed in client-side code. Rotate credentials if exposure is suspected.
Review the services receiving form submissions, the information being collected, data retention practices, and access permissions. Collect only the data required for the intended business purpose.
Periodically review the website's dependencies, publishing access, custom scripts, and connected services. Businesses with specific regulatory or contractual requirements should assess their controls against those requirements.
These steps help businesses address risks that remain relevant regardless of the website platform they use.
Businesses currently running WordPress or another PHP-based platform should prioritize verifying their exposure rather than assuming a migration is the immediate solution.
Recommended actions include:
If a system may have been compromised, patching alone may not be enough. The organization should investigate the incident, determine whether persistence or data exposure occurred, and restore the environment using an appropriate recovery plan.
Refer to the official PHP project and the Wiz PHP2Shell report for current technical guidance.
PHP2Shell refers to two critical PHP runtime vulnerabilities that can enable unauthenticated remote code execution and sensitive process-memory disclosure on affected systems. The issues are tracked as CVE-2026-109618 and CVE-2026-109619.
No. The underlying flaws are in PHP itself, although researchers demonstrated exploitation against WordPress, Drupal, and Joomla environments. Any application using an affected PHP runtime should be assessed according to its actual deployment and configuration.
Standard Webflow-hosted websites do not expose a customer-managed PHP runtime, and Webflow's core hosted services are not built on PHP according to its published security information referenced in reporting on the incident. Other security risks, including account compromise and vulnerabilities in external integrations, still need to be addressed.
No. Webflow's managed hosting reduces certain infrastructure maintenance responsibilities, but it cannot eliminate all risks. Businesses must still secure account access, review custom code, manage external integrations, and protect customer information.
Updating WordPress alone does not fix the underlying PHP runtime vulnerability. The server must run an appropriate patched PHP release or verified security backport. Website owners should coordinate with their hosting provider or technical team.
No. A migration should be based on the business's technical requirements, maintenance capacity, functionality, integrations, budget, and long-term goals. PHP2Shell is a reason to review security responsibilities, not a requirement for every website to change platforms.
PHP2Shell is an important reminder that website security depends on more than the application visible to visitors. Vulnerabilities in the underlying runtime can expose websites even when the application itself has no corresponding coding flaw.
For businesses using PHP-based platforms, the immediate priority is to identify affected environments, apply the appropriate fixes, and investigate any potential compromise.
For organizations planning a new website or evaluating a platform migration, Webflow offers a different operational model. Its managed hosting removes the need for customers to maintain a PHP runtime for standard hosted sites and reduces the burden of routine infrastructure maintenance.
That does not make Webflow invulnerable, but it can simplify the responsibilities a business must manage directly.
At AppsRow, we help businesses build and migrate to Webflow with attention to website structure, integrations, maintainability, and organic search continuity. Choosing the right platform should involve more than responding to one vulnerability. It should support a long-term strategy for building a reliable, manageable, and effective digital presence.
Sandeepsingh Sisodiya is the CEO of Appsrow and a Webflow leader in Ahmedabad, India. He focuses on SaaS growth, digital transformation, and building high-converting website strategies.
CURATED READING

